Na-Mii Dev Team

About Author

Articles by Na-Mii Dev Team

Every major AI platform now ships hooks for agent security. Here’s why they’re the wrong layer for access control – and what goes underneath them.
The same agent that plans a weekend trip can reach company systems, and security teams need a say in what happens next.
An invoice agent can look up a vendor’s prices, but what happens when it tries to change them? The answer starts with its registry entry.
Securing MCP requires a fundamentally different approach than traditional API security.
This tutorial shows how to connect Claude to your macOS filesystem so it can read, write, and do useful things with your data.
Choosing the right flow is only the beginning. The real challenge is implementing either flow without creating persistent credential vulnerabilities that undermine your security.
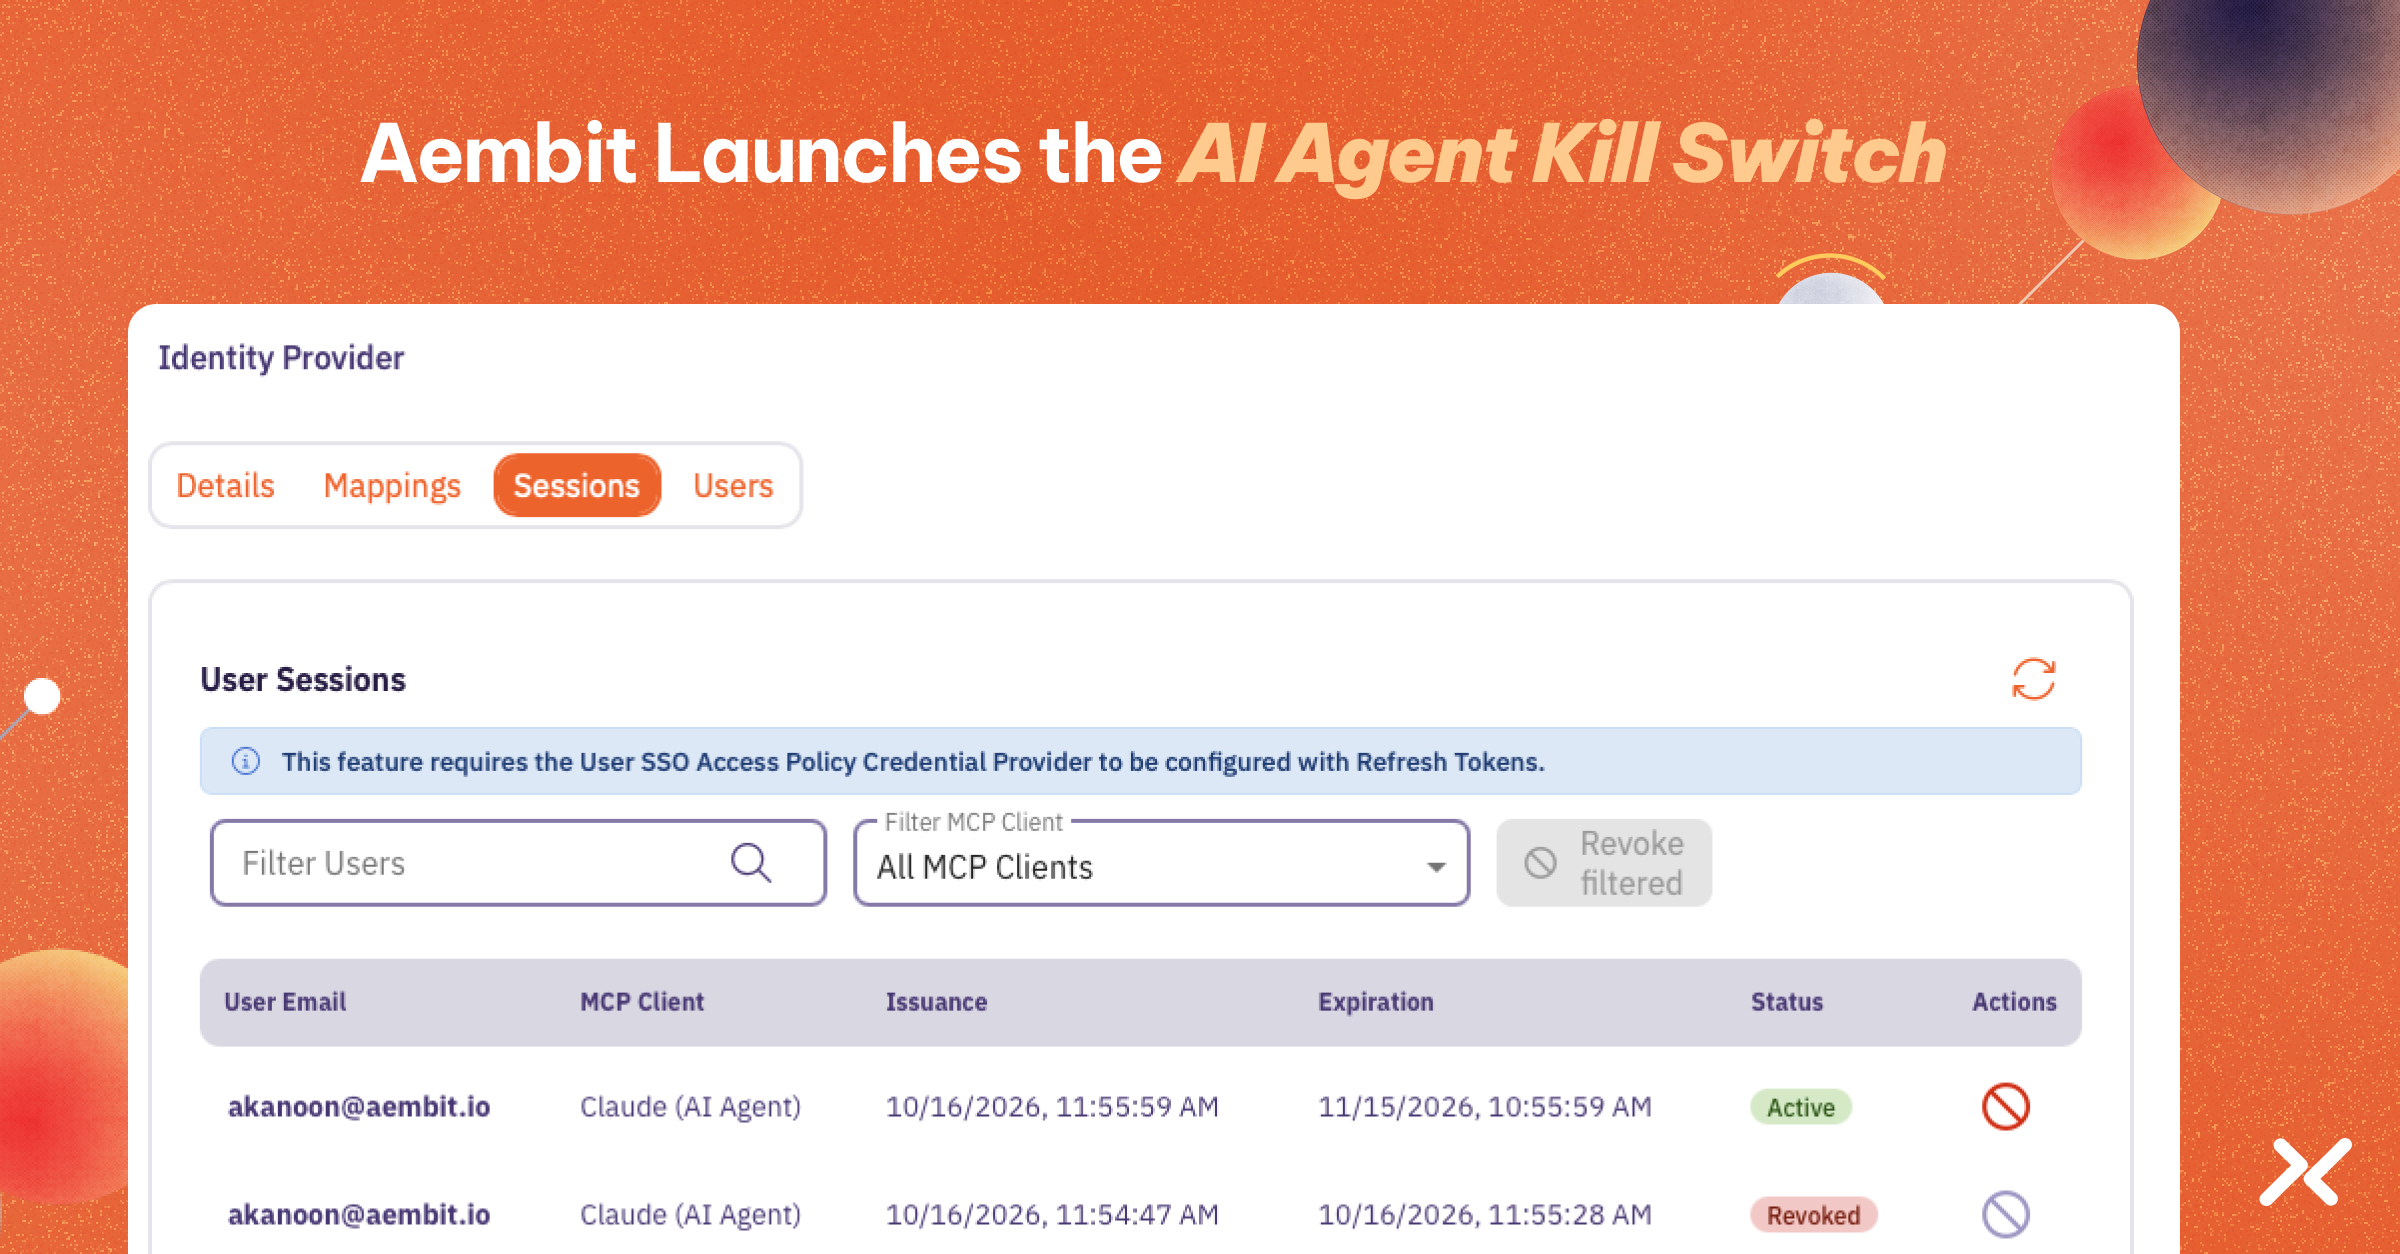
Aembit’s new kill switch lets admins revoke one user’s access through one MCP client, leaving every other agent and user untouched.
Workloads and AI agents can now get both types of SPIFFE credentials through Aembit, freeing teams from deploying and maintaining SPIRE infrastructure.
MCP security is becoming a crowded market of gateways, scanners, access controls, and broader platforms, and the distinctions matter more than the labels.
Everyone wants a kill switch for AI agents, but what actually stops when someone flips it?
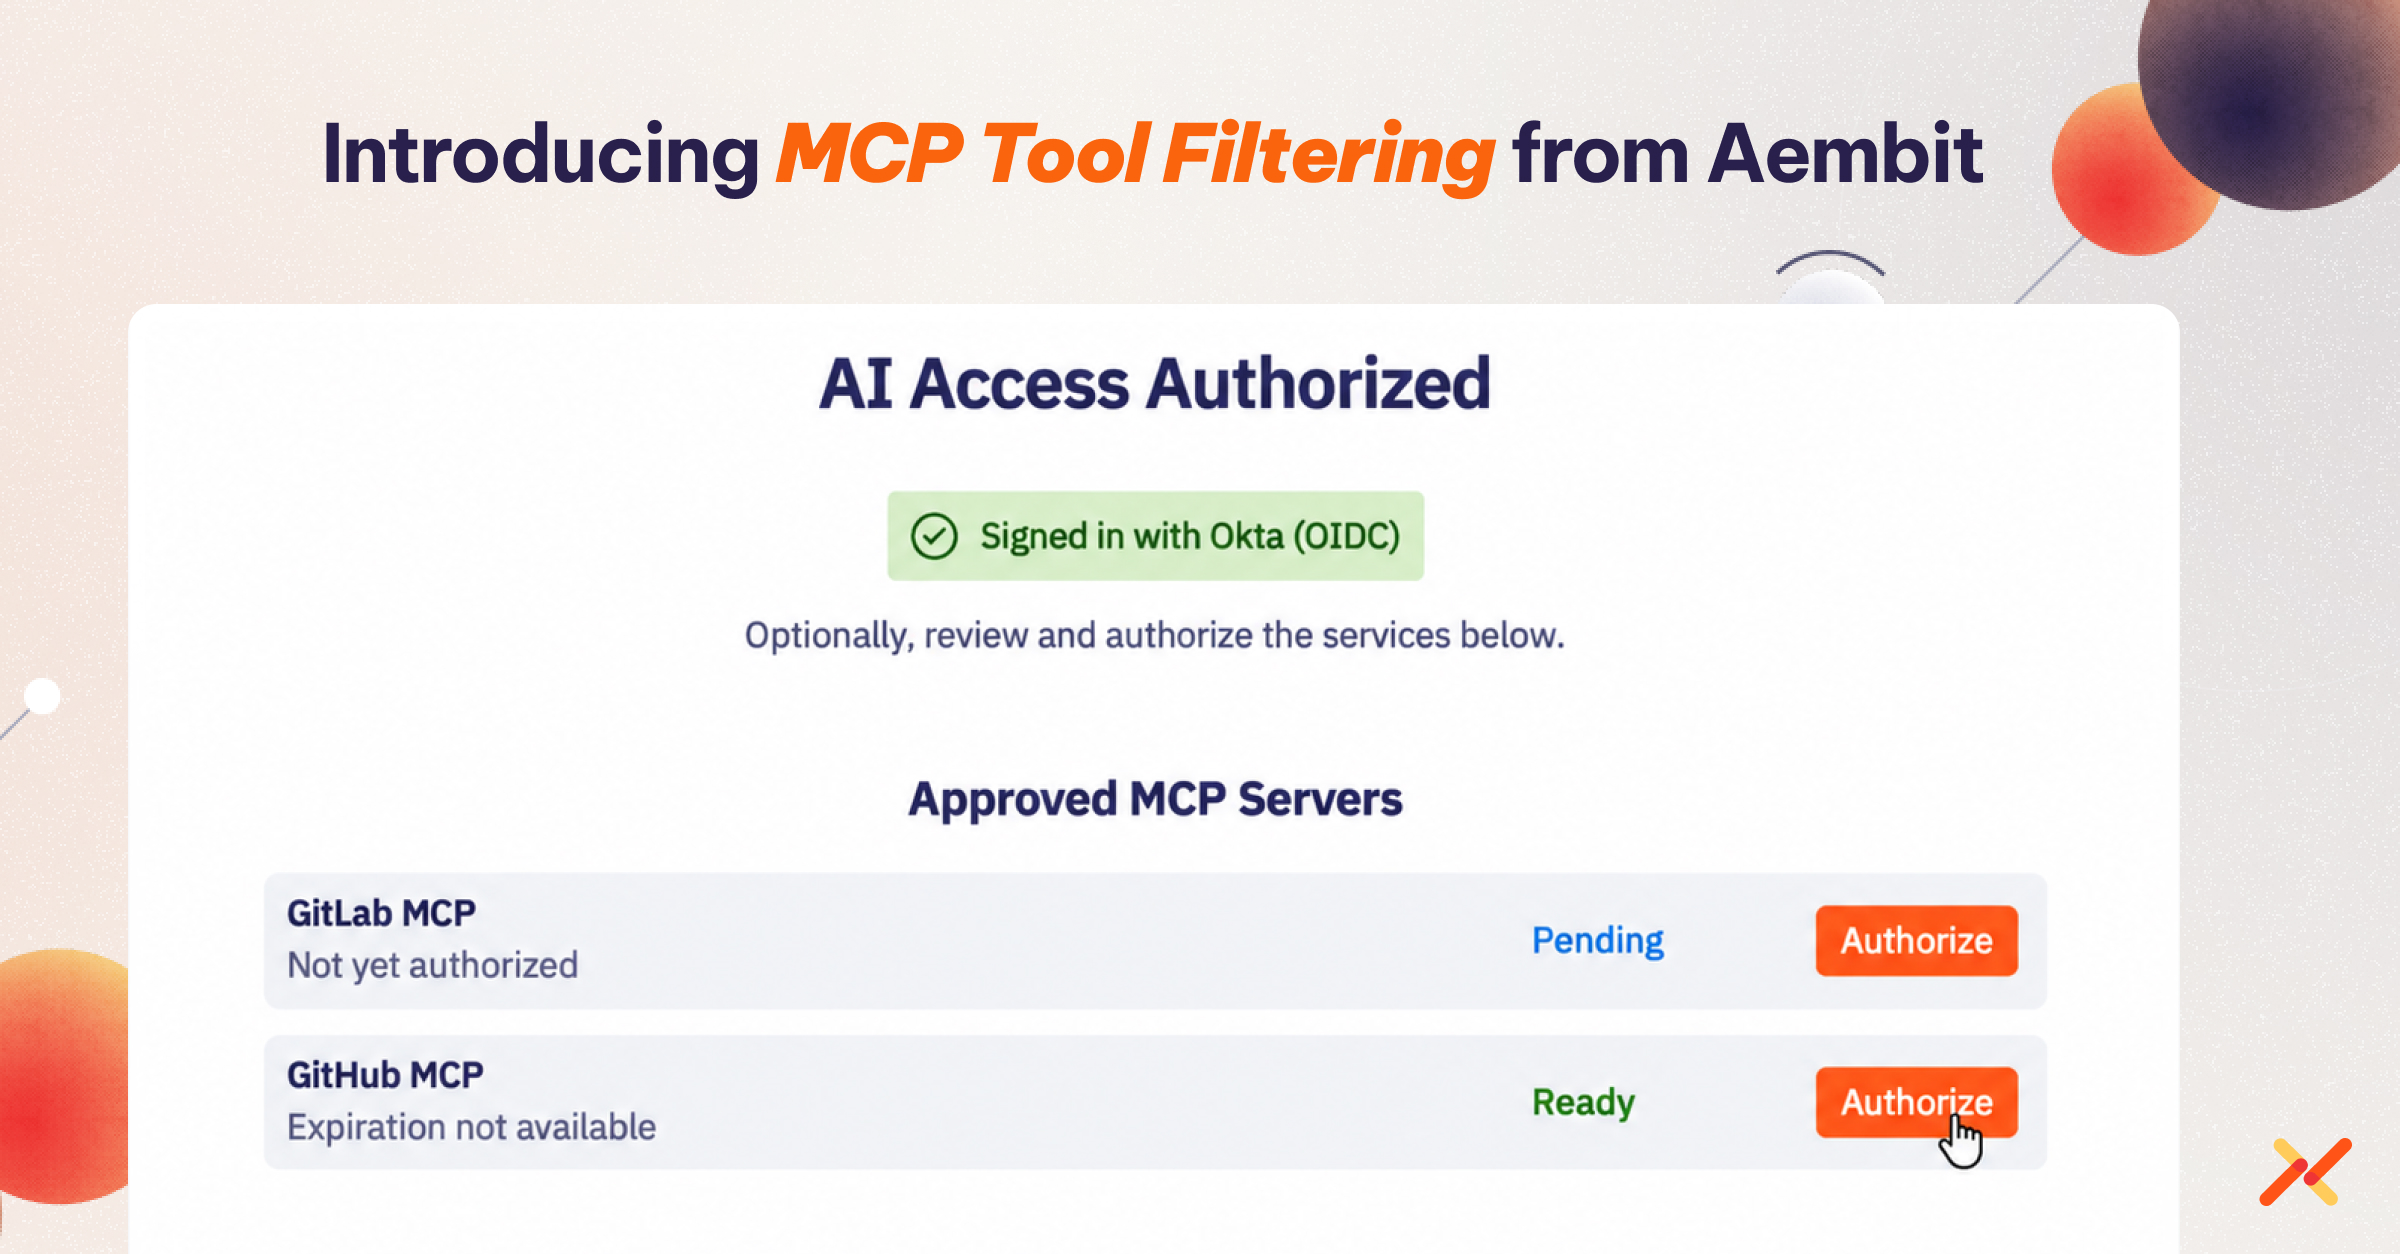
Aembit now lets you allow or block individual MCP tools per agent, not just entire servers. See how tool filtering works.
How to give autonomous agents useful access while preserving identity, accountability, and control.