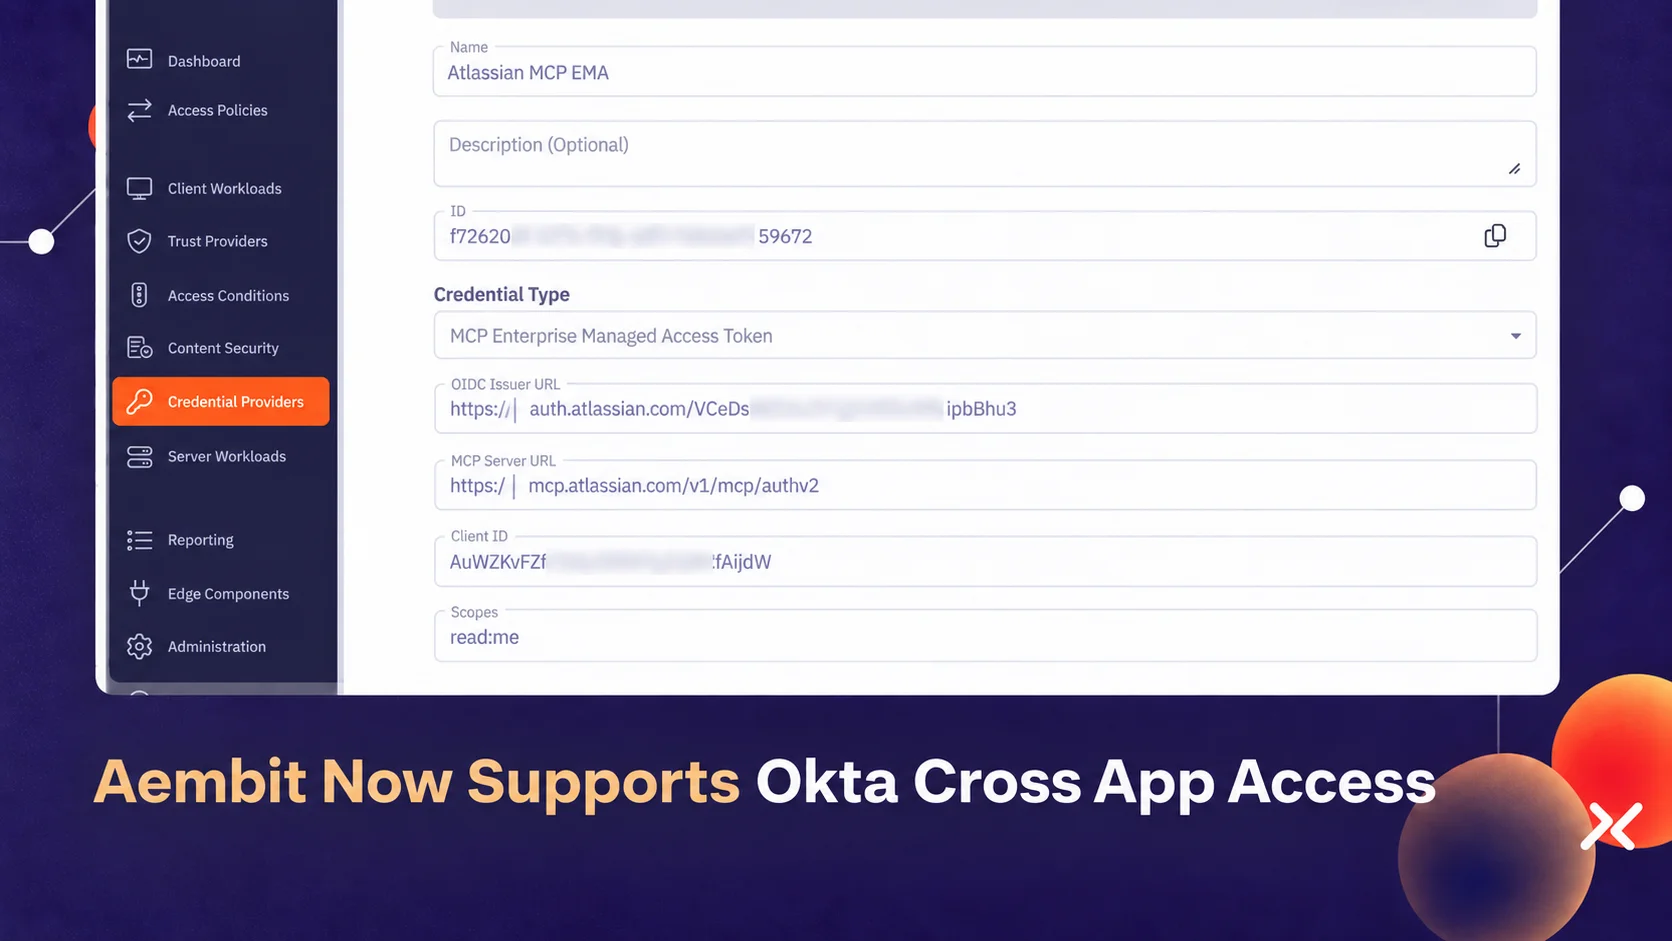
Promotional graphic showing the Aembit dashboard with the Credential Providers section open and an Atlassian MCP EMA configuration form on screen. Some sensitive fields are intentionally blurred. A banner across the bottom reads, “Aembit Now Supports Okta Cross App Access,” set over a dark purple background with abstract connected-line graphics and orange gradient spheres.

4 min readOkta this week is introducing Cross App Access (XAA) at Oktane, a new standard designed to let a user’s existing SSO session authorize downstream applications without requiring a separate consent flow for each one. In the MCP ecosystem, the broader model is known as Enterprise-Managed Authorization (EMA).  We’re launching support for both today as an […]

XAA removes a growing source of agent friction, but uneven support across the enterprise ecosystem makes the transition the harder problem to solve.
Dig in

Recent Stories

When one identity acts for another, the token model determines what downstream systems can actually see, trust, and audit.
Centralized authorization eliminates repeated user consent, but autonomous agents still need runtime policy, short-lived credentials, and audit.
The latest rankings show which risks become more pressing when a model can do more than generate an answer.
Already run CrowdStrike AIDR? See how it builds on Aembit’s identity control plane for AI agents. Read the full breakdown.
An employee, a scheduled agent, and a company-wide assistant may knock on the same MCP server door. They should not get in with the same badge.
OIDC adds identity to OAuth, giving applications a standard way to verify users, receive claims, and support modern sign-on.
Stateless requests, explicit state, and routing metadata bring familiar distributed-systems patterns to agent infrastructure at scale.
The gateway label now covers several very different jobs. The useful question is what traffic each gateway handles, what decision it supports, and where identity and access fit in the architecture.
The second in a five-part series on how MCP is moving beyond tool calling, and what that shift means for agent workflows, interoperability, and enterprise use.
Agentic AI introduces new cybersecurity risks, primarily concerning autonomous identity, tool chain exposure, and cascading compromises, requiring security teams to urgently adopt least-privilege identity frameworks and real-time monitoring designed specifically for self-directed, persistent workloads.
OAuth is an authorization framework that defines how to grant access. JWT is a token format that defines how to package and transmit claims. They solve different problems, and most production systems use both.

Ready to Try Workload IAM?

Get started in minutes, with no sales calls required. Our free-forever tier is just a click away.